Cybersecurity protects your systems. Cybersecurity risk management protects your business.®

The Information Highway

The Information Highway

AI Supply Chain Security: Is Your Business Trusting Tools Noone Has Checked?

ai-supply-chain-security-business

AI supply chain security means protecting your business from risks introduced by artificial intelligence tools, their connected applications, and outside services. An AI assistant may seem like just another productivity tool, but when it can access company email, files, customer records, or business systems, it becomes another connection that needs to be managed and protected.
Continue reading
  496 Hits

Your Team's "Vibe Coded" App Might Already Be Leaking Customer Data

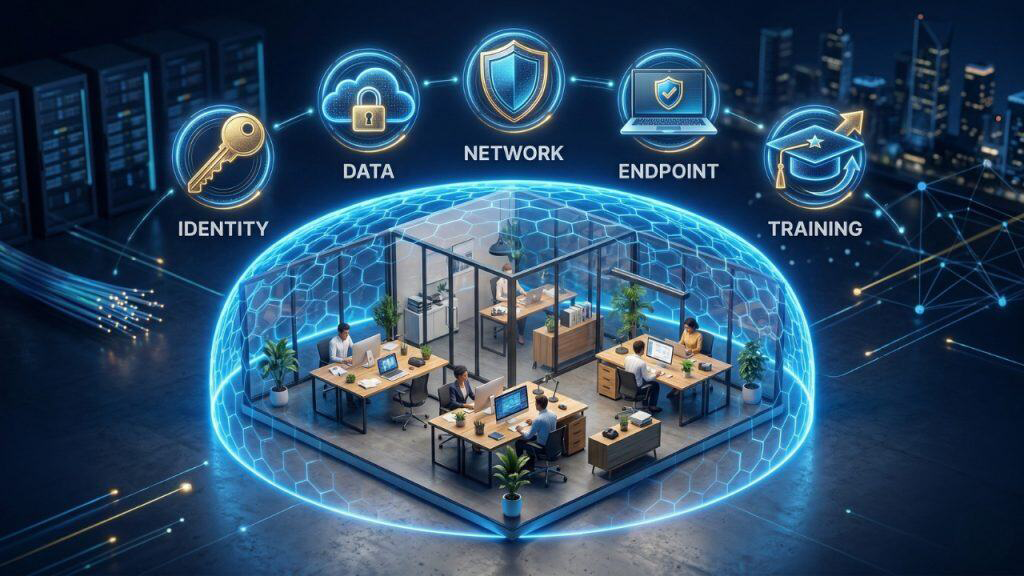
Holographic-Shield-Over-Server-Rack_20261008-101250_1

A single security scan this week found over 16,000 publicly exposed databases built with AI coding tools — a wake-up call that the rush to build fast with AI is quietly creating a breach crisis for businesses of every size, not just tech giants.

Continue reading
  916 Hits

Remote Access Is This Week's Battleground: Here's What Your Business Needs to Know

remoge_access_featured_image
Two fresh warnings, a SANS-flagged wave of attacks abusing legitimate remote-support software and a newly exploited Citrix NetScaler zero-day with a federal patch deadline this week, both target the exact remote-access tools SMBs and their IT providers rely on every day.
Continue reading
  735 Hits

Cybersecurity Threat Advisory: TrustSink Turns Microsoft Entra ID's MFA Against You to Steal Passwords

Threat-Advisory-Banner3

Threat update

Researchers have demonstrated a new attack technique called TrustSink that abuses the multi-factor authentication (MFA) features in Microsoft Entra ID, the identity service behind Microsoft 365. An attacker who gains control of a high-level admin account can quietly add a fake MFA provider to the tenant. From then on, every time a user signs in, that fake provider captures their password in plain text while the login completes normally. Organizations that use Microsoft 365 should review their Entra ID authentication settings and lock down admin accounts now.

Continue reading
  743 Hits

Zimbra Email Servers Hacked Before the Flaw Was Even Announced: What You Need to Know

img-zimbra
A fix for a critical Zimbra email server flaw was available for more than three weeks before the public was told about it, and attackers used that time. Microsoft Threat Intelligence reports that threat actors exploited CVE-2026-73570 (CVSS 8.9), an unauthenticated operating system command injection vulnerability in the Zimbra Collaboration Suite, for weeks before it was disclosed. The Shadowserver Foundation counted 274 compromised Zimbra servers in a single recent week.
Continue reading
  612 Hits

Top Breaches Cost ($) of 2024

HEALTHCARE
FINANCIAL
INDUSTRIAL
TECHNOLOGY
ENERGY
Source: IBM Cost of a Data Breach Report 2024