
On the first day of Pwn2Own Vancouver 2024, contestants demoed 19 zero-day vulnerabilities in Windows 11, Tesla, Ubuntu Linux and other devices and software to win $732,500 and a Tesla Model 3 car.

A live, actively targetable flaw in on-premises Microsoft Exchange is sitting unpatched on roughly 22,000 servers worldwide and for many small and mid-size businesses, the safety net (extended security support) runs out next month, turning a patching task into a hard deadline.
If you've been preparing your company for a CMMC Level 2 certification assessment, you may have heard some confusing news: the federal government has put CMMC Phase II on hold.
That part is true.
What isn't true is that CMMC has disappeared.
On July 13, 2026, the Department announced the immediate suspension of CMMC Phase II, which had been scheduled to begin November 10, 2026. At the same time, officials launched a 60-day review of the program. Phase I self-assessment requirements remain in place.
AI phishing attacks are making familiar cyber scams faster, more convincing, and harder for employees to recognize. Recent 2026 threat intelligence shows attackers expanding beyond email into Microsoft Teams, voice calls, trusted cloud services, and highly personalized messages. For businesses, protecting Microsoft 365 identities and training employees to verify unusual requests has become increasingly important.
Microsoft has confirmed that last month's Windows security updates are breaking SSH connections on some Windows 11 22H2 and 23H2 systems.
More than 60,000 D-Link network-attached storage devices that have reached end-of-life are vulnerable to a command injection vulnerability with a publicly available exploit.
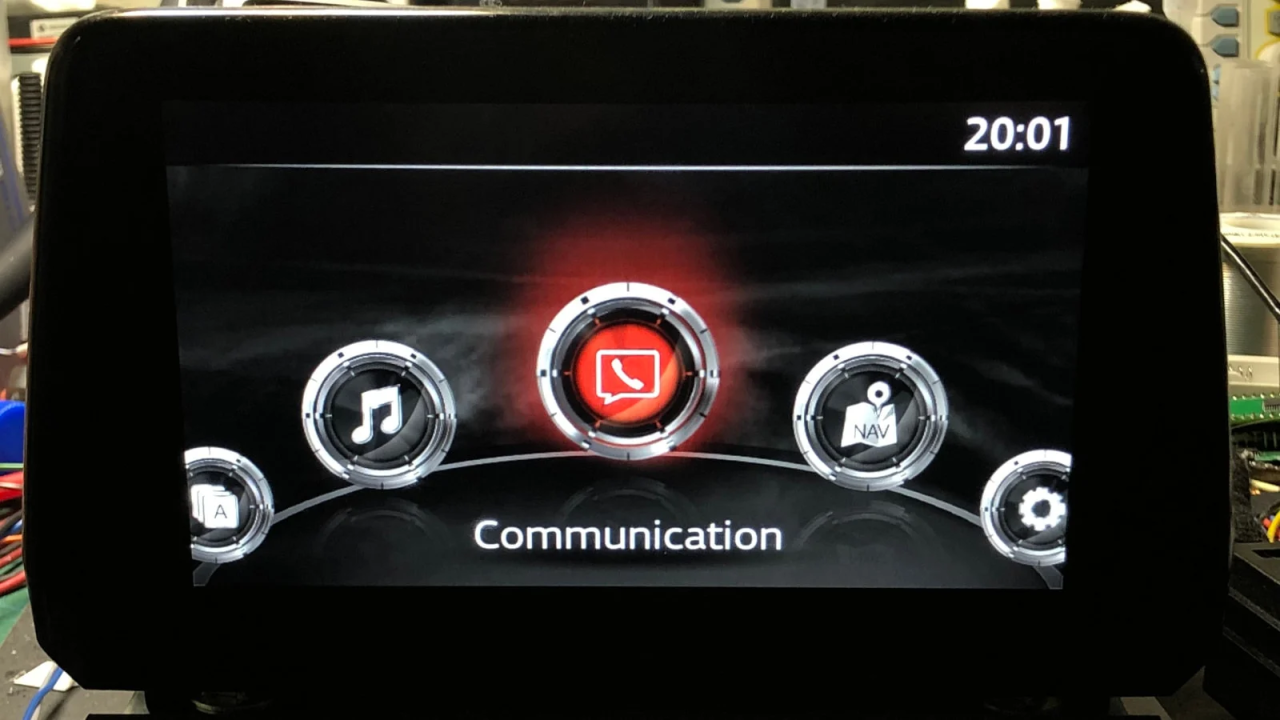
Attackers could exploit several vulnerabilities in the Mazda Connect infotainment unit, present in multiple car models including Mazda 3 (2014-2021), to execute arbitrary code with root permission.
On the first day of Pwn2Own Vancouver 2024, contestants demoed 19 zero-day vulnerabilities in Windows 11, Tesla, Ubuntu Linux and other devices and software to win $732,500 and a Tesla Model 3 car.

Fortinet has released security updates for an unauthorized code execution vulnerability impacting their FortiClientEMS (Endpoint Management Server) product. The vulnerability, CVE-2023-48788, is related to a flaw that allows unauthenticated malicious actors to execute code or commands onto the server via purposely crafted requests. This Cybersecurity Threat Advisory highlights various recommendations to mitigate the potential impact on your devices.
A critical vulnerability (CVE-2024-1403) affecting Progress Software OpenEdge Authentication Gateway and AdminServer impacts versions 11.7.18 and earlier, 12.2.13 and earlier, and 12.8.0. The vulnerability allows unauthorized access due to manipulation of username and password combinations during the authentication process. Review this Cybersecurity Threat Advisory to minimize the potential impact on your systems.
A critical vulnerability is affecting many Fortinet devices. Approximately 150,000 Fortinet OS and FortiProxy Secure Web Gateway systems are believed to be exposed to this flaw. Continue reading this Cybersecurity Threat Advisory to learn how you can mitigate the potential risk and impact of this vulnerability.

Microsoft announced that Office LTSC 2024, the next Office LTSC release, will enter a commercial preview phase starting next month and will be generally available later this year.
Necessary cookies support essential features such as secure sessions and forms. Analytics is optional and stays off unless you allow it.
Required for core site functions, security, and preferences.