The Securities and Exchange Commission (SEC) has adopted amendments to Regulation S-P that require certain financial institutions to disclose data breach incidents to impacted individuals within 30 days of discovery.

When a single ransomware attack can cancel surgeries, divert ambulances, and cancel classes within hours, "we're too small to be a target" stops being a credible security strategy for any organization including yours.
We have some good news to share: as of Wednesday, September 30, 2026, LBT Technology Group, LLC is officially SPECTRA Certified.
If you've never heard of SPECTRA, you're not alone. Most business owners don't spend their days thinking about IT certifications, and they shouldn't have to. That's our job. But this one is worth a few minutes of your time, because it affects how well your business is protected, and it may even lower what you pay for cyber insurance.
In this post, we'll explain what SPECTRA Certification is, what we had to prove to earn it, and what it means for you, whether you're already a client or you're looking for an IT partner.
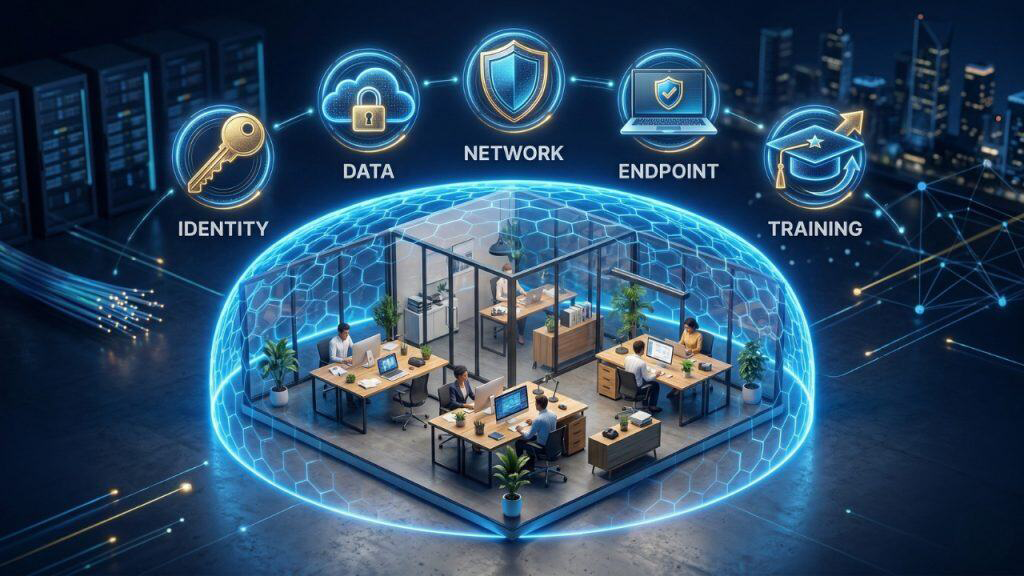
AI phishing attacks are making familiar cyber scams faster, more convincing, and harder for employees to recognize. Recent 2026 threat intelligence shows attackers expanding beyond email into Microsoft Teams, voice calls, trusted cloud services, and highly personalized messages. For businesses, protecting Microsoft 365 identities and training employees to verify unusual requests has become increasingly important.
The Securities and Exchange Commission (SEC) has adopted amendments to Regulation S-P that require certain financial institutions to disclose data breach incidents to impacted individuals within 30 days of discovery.
The WebTPA Employer Services (WebTPA) data breach disclosed earlier this month is impacting close to 2.5 million individuals, the U.S. Department of Health and Human Services notes.
The Norwegian National Cyber Security Centre (NCSC) recommends replacing SSLVPN/WebVPN solutions with alternatives due to the repeated exploitation of related vulnerabilities in edge network devices to breach corporate networks.
Electronic prescription provider MediSecure in Australia has shut down its website and phone lines following a ransomware attack believed to originate from a third-party vendor.
This Cybersecurity Threat Advisory breaks down multiple critical vulnerabilities in the Cacti framework, an open-source network monitoring and fault management tool. Successful exploitation of these vulnerabilities could allow attackers to execute arbitrary code and compromise network infrastructure.
Necessary cookies support essential features such as secure sessions and forms. Analytics is optional and stays off unless you allow it.
Required for core site functions, security, and preferences.