A new ransomware operation named 'Fog' launched in early May 2024, is using compromised VPN credentials to breach the networks of educational organizations in the U.S.

A live, actively targetable flaw in on-premises Microsoft Exchange is sitting unpatched on roughly 22,000 servers worldwide and for many small and mid-size businesses, the safety net (extended security support) runs out next month, turning a patching task into a hard deadline.
If you've been preparing your company for a CMMC Level 2 certification assessment, you may have heard some confusing news: the federal government has put CMMC Phase II on hold.
That part is true.
What isn't true is that CMMC has disappeared.
On July 13, 2026, the Department announced the immediate suspension of CMMC Phase II, which had been scheduled to begin November 10, 2026. At the same time, officials launched a 60-day review of the program. Phase I self-assessment requirements remain in place.
AI phishing attacks are making familiar cyber scams faster, more convincing, and harder for employees to recognize. Recent 2026 threat intelligence shows attackers expanding beyond email into Microsoft Teams, voice calls, trusted cloud services, and highly personalized messages. For businesses, protecting Microsoft 365 identities and training employees to verify unusual requests has become increasingly important.
Microsoft has confirmed that last month's Windows security updates are breaking SSH connections on some Windows 11 22H2 and 23H2 systems.
More than 60,000 D-Link network-attached storage devices that have reached end-of-life are vulnerable to a command injection vulnerability with a publicly available exploit.
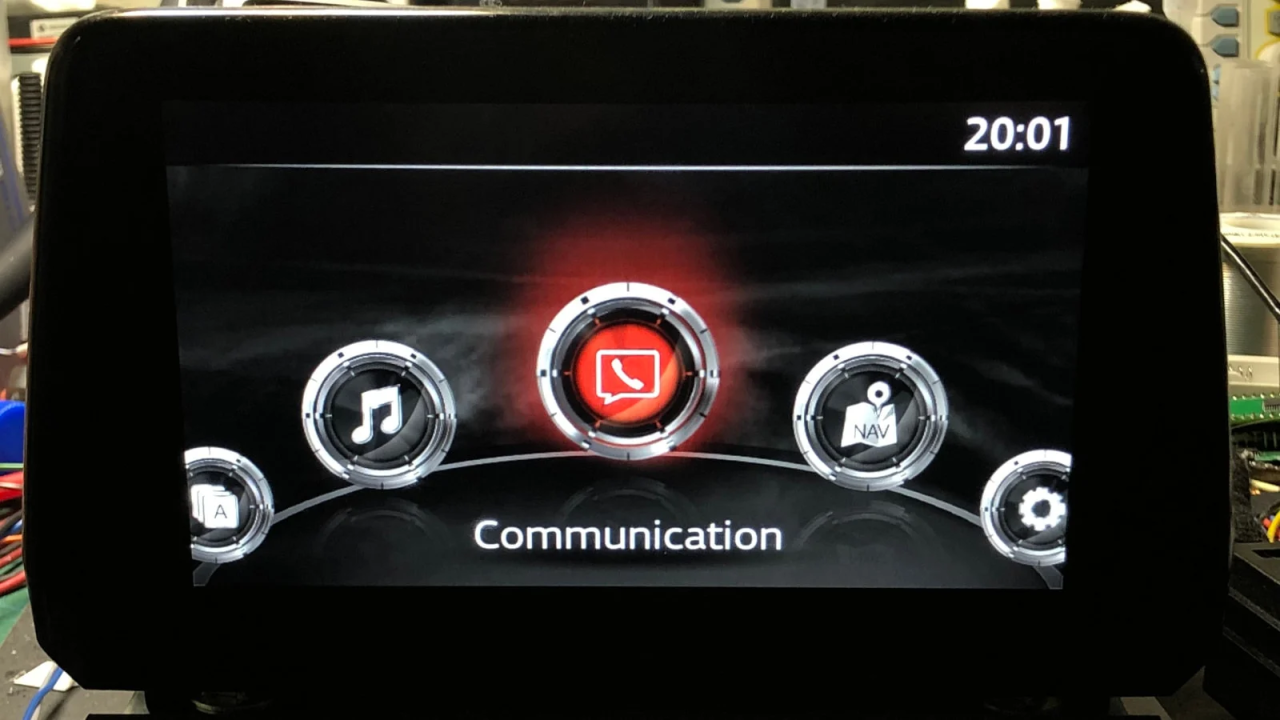
Attackers could exploit several vulnerabilities in the Mazda Connect infotainment unit, present in multiple car models including Mazda 3 (2014-2021), to execute arbitrary code with root permission.
A new ransomware operation named 'Fog' launched in early May 2024, is using compromised VPN credentials to breach the networks of educational organizations in the U.S.
Palo Alto Networks has recently disclosed a critical zero-day vulnerability, CVE-2024-3400, within its PAN-OS operating system. The flaw, found in the GlobalProtect Gateway, is currently under active exploitation. Additionally, the threat actors behind RedTail cryptocurrency mining malware have added this vulnerability to its exploit arsenal, further intensifying the threat.
A new PHP for Windows remote code execution (RCE) vulnerability has been disclosed, impacting all releases since version 5.x, potentially impacting a massive number of servers worldwide.
The FBI urges past victims of LockBit ransomware attacks to come forward after revealing that it has obtained over 7,000 LockBit decryption keys that they can use to recover encrypted data for free.
Threat actors claim to be selling 3TB of data from Advance Auto Parts, a leading automotive aftermarket parts provider, stolen after breaching the company's Snowflake account.
Necessary cookies support essential features such as secure sessions and forms. Analytics is optional and stays off unless you allow it.
Required for core site functions, security, and preferences.