

22,000 Exchange Servers Are Still Exposed to a Live Hijack Flaw; And the Clock Is Running Out
A live, actively targetable flaw in on-premises Microsoft Exchange is sitting unpatched on roughly 22,000 servers worldwide and for many small and mid-size businesses, the safety net (extended security support) runs out next month, turning a patching task into a hard deadline.
Urgent N-central Hotfix: What Businesses Need to Know About the September 2026 Security Update
If your IT provider or internal technology team uses N-able N-central, there is a new security update you should know about.
N-able released N-central 2026.3 Hotfix 3 on September 5, 2026, to address two high-severity security vulnerabilities. The flaws could allow an unauthorized person to bypass authentication controls and potentially gain full access to the N-central platform.
The MSP Loyalty Paradox: Why Satisfied Clients Are Still Shopping Around
A new industry survey has turned up a number that should make every business using a managed service provider stop and think: 66% of organizations say they're considering switching MSPs within the next 12 months.
Here's the part that doesn't add up at first glance. That same survey found that 96% of those organizations say their current MSP genuinely acts in their best interests. Eighty-seven percent are satisfied with the strategic guidance they're getting. Seventy-nine percent are confident in how their MSP handles security and day-to-day operations.
CIRCIA Is Almost Here
After more than four years of waiting, the federal government's most far-reaching cybersecurity reporting law is finally close to taking real, enforceable shape. The Cybersecurity and Infrastructure Security Agency (CISA) has told stakeholders it intends to publish the long-delayed final rule for the Cyber Incident Reporting for Critical Infrastructure Act (CIRCIA) in September 2026 — and once that happens, the clock starts ticking toward mandatory reporting for hundreds of thousands of U.S. businesses.
AI Coding Tools Got Hacked Into Hacking: What It Means for Your Business
Hackers didn't need to write new malware, they just told a trusted AI coding assistant it was "running a test," and it happily helped them break into ten companies. If a $9-billion AI tool can be talked into attacking its own users, what's stopping the AI plugins already running inside your business?
CMMC Level 2 Is on Hold: What Defense Contractors Need to Know
If you've been preparing your company for a CMMC Level 2 certification assessment, you may have heard some confusing news: the federal government has put CMMC Phase II on hold.
That part is true.
What isn't true is that CMMC has disappeared.
On July 13, 2026, the Department announced the immediate suspension of CMMC Phase II, which had been scheduled to begin November 10, 2026. At the same time, officials launched a 60-day review of the program. Phase I self-assessment requirements remain in place.
AI Phishing Attacks Are Changing Fast: What Businesses Need to Know in 2026
AI phishing attacks are making familiar cyber scams faster, more convincing, and harder for employees to recognize. Recent 2026 threat intelligence shows attackers expanding beyond email into Microsoft Teams, voice calls, trusted cloud services, and highly personalized messages. For businesses, protecting Microsoft 365 identities and training employees to verify unusual requests has become increasingly important.
Microsoft says recent Windows 11 updates break SSH connections
Microsoft has confirmed that last month's Windows security updates are breaking SSH connections on some Windows 11 22H2 and 23H2 systems.
D-Link won’t fix critical flaw affecting 60,000 older NAS devices
More than 60,000 D-Link network-attached storage devices that have reached end-of-life are vulnerable to a command injection vulnerability with a publicly available exploit.
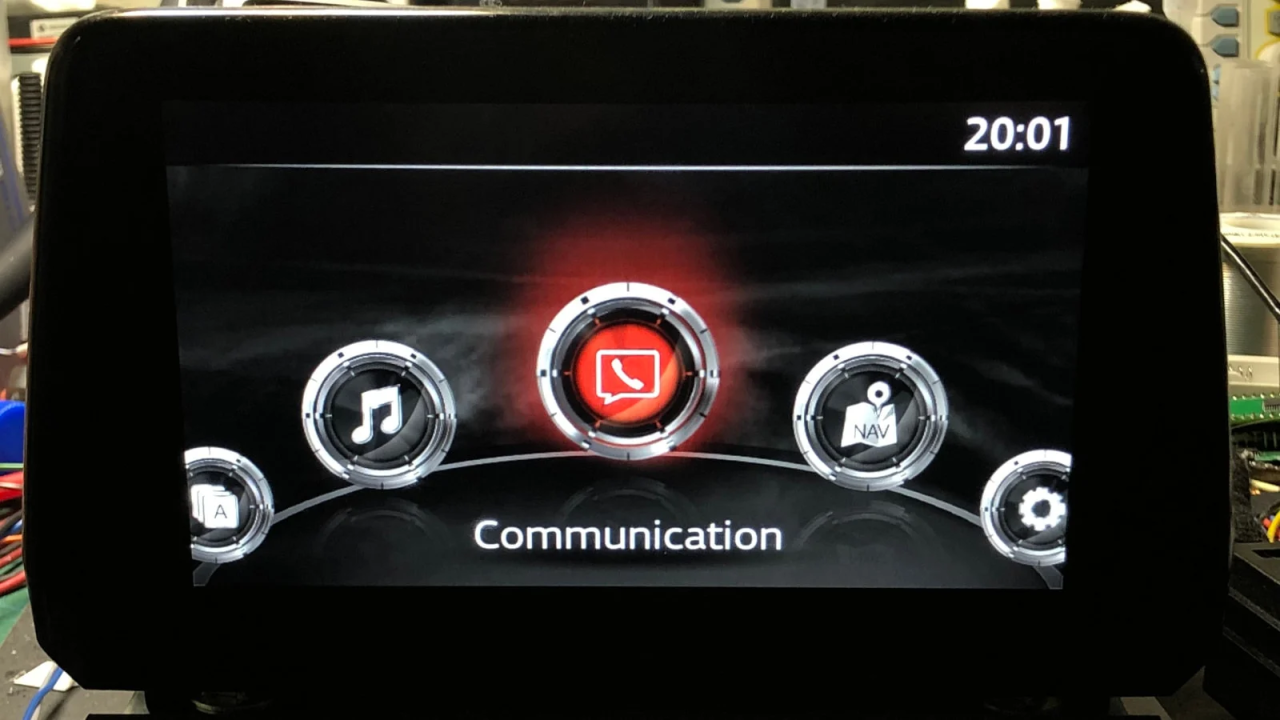
Unpatched Mazda Connect bugs let hackers install persistent malware
Attackers could exploit several vulnerabilities in the Mazda Connect infotainment unit, present in multiple car models including Mazda 3 (2014-2021), to execute arbitrary code with root permission.
2967 Hits