Microsoft has started rolling out its Copilot AI assistant to Windows 10 with the KB5032278 November 2023 non-security preview update for systems running Windows 10, version 22H2.


Microsoft has started rolling out its Copilot AI assistant to Windows 10 with the KB5032278 November 2023 non-security preview update for systems running Windows 10, version 22H2.
Apple released emergency security updates to fix two zero-day vulnerabilities exploited in attacks and impacting iPhone, iPad, and Mac devices, reaching 20 zero-days patched since the start of the year.
Multiple security vulnerabilities collectively named LogoFAIL affect image-parsing components in the UEFI code from various vendors. Researchers warn that they could be exploited to hijack the execution flow of the booting process and to deliver bootkits.
Microsoft has started testing a new Windows 11 Energy Saver feature that helps customers extend their portable computers' battery life.

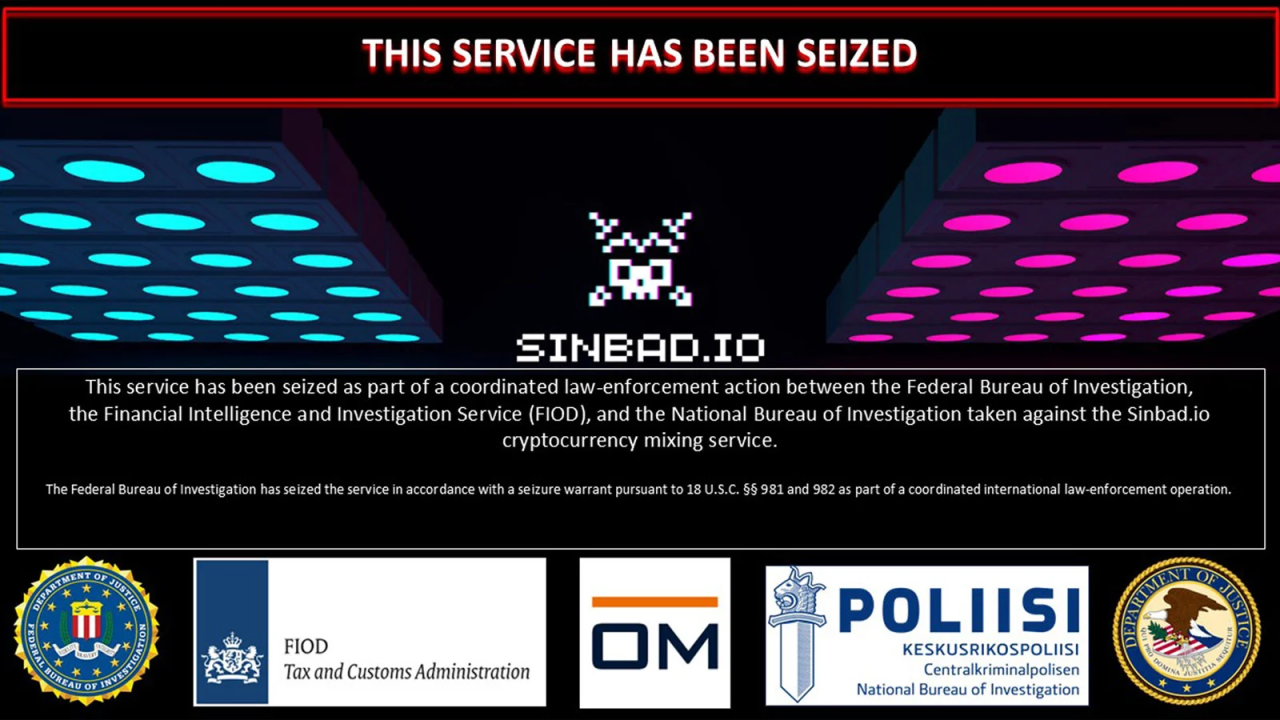
The U.S. Department of the Treasury has sanctioned the Sinbad cryptocurrency mixing service for its use as a money-laundering tool by the North Korean Lazarus hacking group.
Google has fixed the sixth Chrome zero-day vulnerability this year in an emergency security update released today to counter ongoing exploitation in attacks.
Today, Microsoft shared a temporary fix for a known issue causing Outlook Desktop to crash when sending emails from Outlook.com accounts.
Security researchers bypassed Windows Hello fingerprint authentication on Dell Inspiron, Lenovo ThinkPad, and Microsoft Surface Pro X laptops in attacks exploiting security flaws found in the embedded fingerprint sensors.
The Idaho National Laboratory (INL) confirms they suffered a cyberattack after 'SiegedSec' hacktivists leaked stolen human resources data online.
Microsoft has unveiled a new bug bounty program aimed at the Microsoft Defender security platform, with rewards between $500 and $20,000.
AutoZone is warning tens of thousands of its customers that it suffered a data breach as part of the Clop MOVEit file transfer attacks.
Citrix reminded admins today that they must take additional measures after patching their NetScaler appliances against the CVE-2023-4966 'Citrix Bleed' vulnerability to secure vulnerable devices against attacks.

The former chief operating officer of a cybersecurity company has pleaded guilty to hacking two hospitals, part of the Gwinnett Medical Center (GMC), in June 2021 to boost his company's business.
The Lumma information-stealing malware is now using an interesting tactic to evade detection by security software - the measuring of mouse movements using trigonometry to determine if the malware is running on a real machine or an antivirus sandbox.
A team of academic researchers from universities in California and Massachusetts demonstrated that it's possible under certain conditions for passive network attackers to retrieve secret RSA keys from naturally occurring errors leading to failed SSH (secure shell) connection attempts.

Microsoft announced a new policy that allows admins to control how optional updates are deployed on Windows 10 enterprise endpoints on their networks.

The Federal Communications Commission (FCC) has revealed new rules to shield consumers from criminals who hijack their phone numbers in SIM swapping attacks and port-out fraud.


Google has officially announced plans to gradually eliminate third-party cookies, a key aspect of its Privacy Sandbox initiative.
The U.S. Cybersecurity & Infrastructure Security Agency has added to its catalog of known exploited vulnerabilities (KEV) three security issues that affect Microsoft devices, a Sophos product, and an enterprise solution from Oracle.

Microsoft will roll out the Copilot AI-powered assistant to Windows 10 systems enrolled in the Insider Program over the coming months.
Necessary cookies support essential features such as secure sessions and forms. Analytics is optional and stays off unless you allow it.
Required for core site functions, security, and preferences.