Hackers are exploiting a critical vulnerability that affects all D-Link DIR-859 WiFi routers to collect account information from the device, including passwords.

Hackers are exploiting a critical vulnerability that affects all D-Link DIR-859 WiFi routers to collect account information from the device, including passwords.
Hackers are exploiting a flaw in a premium Facebook module for PrestaShop named pkfacebook to deploy a card skimmer on vulnerable e-commerce sites and steal people's payment credit card details.


The Treasury Department's Office of Foreign Assets Control (OFAC) has sanctioned twelve Kaspersky Lab executives for operating in the technology sector of Russia.
UnitedHealth has confirmed for the first time what types of medical and patient data were stolen in the massive Change Healthcare ransomware attack, stating that data breach notifications will be mailed in July.

CDK Global has cautioned customers about unscrupulous actors calling them and posing as CDK agents or affiliates to gain unauthorized systems access.
A newly discovered vulnerability in Phoenix SecureCore UEFI firmware tracked as CVE-2024-0762 impacts devices running numerous Intel CPUs, with Lenovo already releasing new firmware updates to resolve the flaw.
T-Mobile has denied it was breached or that source code was stolen after a threat actor claimed to be selling stolen data from the telecommunications company.

Microsoft has announced new cybersecurity enhancements for Outlook personal email accounts as part of its 'Secure Future Initiative,' including the deprecation of basic authentication (username + password) by September 16, 2024.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a high-severity Windows vulnerability abused in ransomware attacks as a zero-day to its catalog of actively exploited security bugs.
American financial services holding company Globe Life says attackers may have accessed consumer and policyholder data after breaching one of its web portals.
Microsoft is delaying the release of its AI-powered Windows Recall feature to test and secure it further before releasing it in a public preview on Copilot+ PCs.
Internal source code and data belonging to The New York Times was leaked on the 4chan message board after being stolen from the company's GitHub repositories in January 2024, The Times confirmed.
LastPass says its almost 12-hour outage yesterday was caused by a bad update to its Google Chrome extension.
Apple will reportedly unveil a standalone password manager named 'Passwords' as part of iOS 18, iPadOS 18, and macOS 15 during the upcoming Apple Worldwide Developers Conference.
Frontier Communications is warning 750,000 customers that their information was exposed in a data breach after an April cyberattack claimed by the RansomHub ransomware operation.
The FBI urges past victims of LockBit ransomware attacks to come forward after revealing that it has obtained over 7,000 LockBit decryption keys that they can use to recover encrypted data for free.
Threat actors claim to be selling 3TB of data from Advance Auto Parts, a leading automotive aftermarket parts provider, stolen after breaching the company's Snowflake account.
Ariane Systems self check-in systems installed at thousands of hotels worldwide are vulnerable to a kiosk mode bypass flaw that could allow access to guests' personal information and the keys for other rooms.
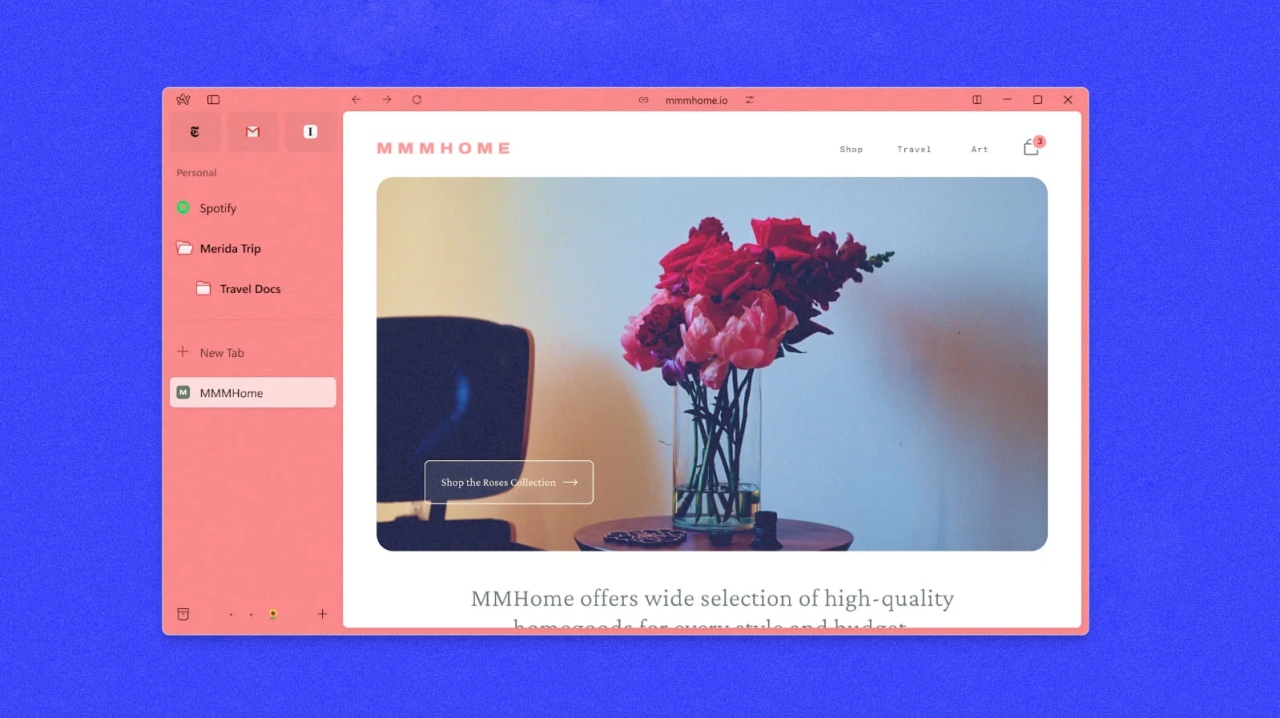
A new Google Ads malvertising campaign, coinciding with the launch of the Arc web browser for Windows, was tricking people into downloading trojanized installers that infect them with malware payloads.
Microsoft says the Cortana, Tips, and WordPad applications will be automatically removed on systems upgraded to the upcoming Windows 11 24H2 release.
Necessary cookies support essential features such as secure sessions and forms. Analytics is optional and stays off unless you allow it.
Required for core site functions, security, and preferences.