
Microsoft is investigating Exchange Online mail delivery issues causing "Server busy" errors and delays when receiving emails from outside organizations.

A live, actively targetable flaw in on-premises Microsoft Exchange is sitting unpatched on roughly 22,000 servers worldwide and for many small and mid-size businesses, the safety net (extended security support) runs out next month, turning a patching task into a hard deadline.
If you've been preparing your company for a CMMC Level 2 certification assessment, you may have heard some confusing news: the federal government has put CMMC Phase II on hold.
That part is true.
What isn't true is that CMMC has disappeared.
On July 13, 2026, the Department announced the immediate suspension of CMMC Phase II, which had been scheduled to begin November 10, 2026. At the same time, officials launched a 60-day review of the program. Phase I self-assessment requirements remain in place.
AI phishing attacks are making familiar cyber scams faster, more convincing, and harder for employees to recognize. Recent 2026 threat intelligence shows attackers expanding beyond email into Microsoft Teams, voice calls, trusted cloud services, and highly personalized messages. For businesses, protecting Microsoft 365 identities and training employees to verify unusual requests has become increasingly important.
Microsoft has confirmed that last month's Windows security updates are breaking SSH connections on some Windows 11 22H2 and 23H2 systems.
More than 60,000 D-Link network-attached storage devices that have reached end-of-life are vulnerable to a command injection vulnerability with a publicly available exploit.
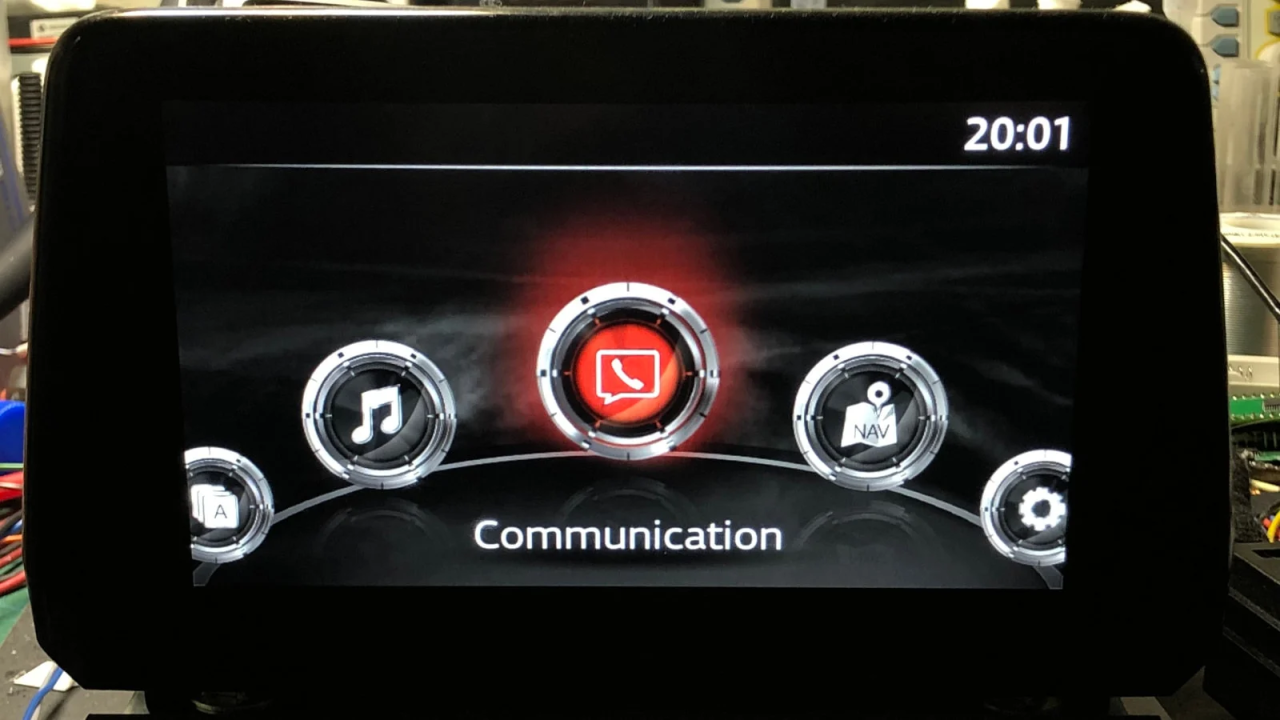
Attackers could exploit several vulnerabilities in the Mazda Connect infotainment unit, present in multiple car models including Mazda 3 (2014-2021), to execute arbitrary code with root permission.
Microsoft is investigating Exchange Online mail delivery issues causing "Server busy" errors and delays when receiving emails from outside organizations.
Microsoft says a Chinese-backed threat group tracked as 'Storm-0062' (aka DarkShadow or Oro0lxy) has been exploiting a critical privilege escalation zero-day in the Atlassian Confluence Data Center and Server since September 14, 2023.
Hackers are once again abusing LinkedIn Smart Links in phishing attacks to bypass protection measures and evade detection in attempts to steal Microsoft account credentials.

Microsoft warned customers this week of incorrect BitLocker drive encryption errors being shown in some managed Windows environments.
A Mirai-based DDoS (distributed denial of service) malware botnet tracked as IZ1H9 has added thirteen new payloads to target Linux-based routers and routers from D-Link, Zyxel, TP-Link, TOTOLINK, and others.
Necessary cookies support essential features such as secure sessions and forms. Analytics is optional and stays off unless you allow it.
Required for core site functions, security, and preferences.